A code audit that shows what your product is really built on, before it costs you.
A senior, written code audit of your codebase, architecture and team, from a sitting CTO who still writes code. You'll know what's solid, what's risky and what will break first, ranked by business impact, with a clear call: fix, refactor or rebuild.
Technology leadership for
 Satsman
Founders who need an honest answer about what they have
For a live or in-progress product, when you need a senior answer you can act on rather than another opinion.
Built with AI tools
Your product came together in Lovable, Bolt, Replit or Cursor, and you are not sure it will hold up with real users, real data and real money.
Built by an agency or freelancer
Someone else wrote the code, and you have no way to judge whether it is good, or whether you are getting what you are paying for.
A product that has slowed down
Features take longer than they used to, bugs keep coming back, and nobody can tell you why.
Before you raise, hire or rebuild
You are about to put money or people behind the codebase, and you want a senior read on it first, before an investor’s technical due diligence gives you one.
A code audit of the parts that decide whether a product holds up
I read the code, the infrastructure and the way the work is being delivered, not just a checklist of tools.
- Codebase and architecture
- Data model
- Authentication and access control
- Multi-tenancy
- Security basics: secrets, permissions, dependencies
- Infrastructure and deployment
- Scalability limits
- Code quality and test coverage
- Whether the team or vendor is on track
What the report looks like
Every report follows the same structure, written so a non-technical founder can act on it and a technical one can check it. This sample is based on a real engagement: a Bitcoin education platform built by its founder on Replit, with the client’s name and some details changed.
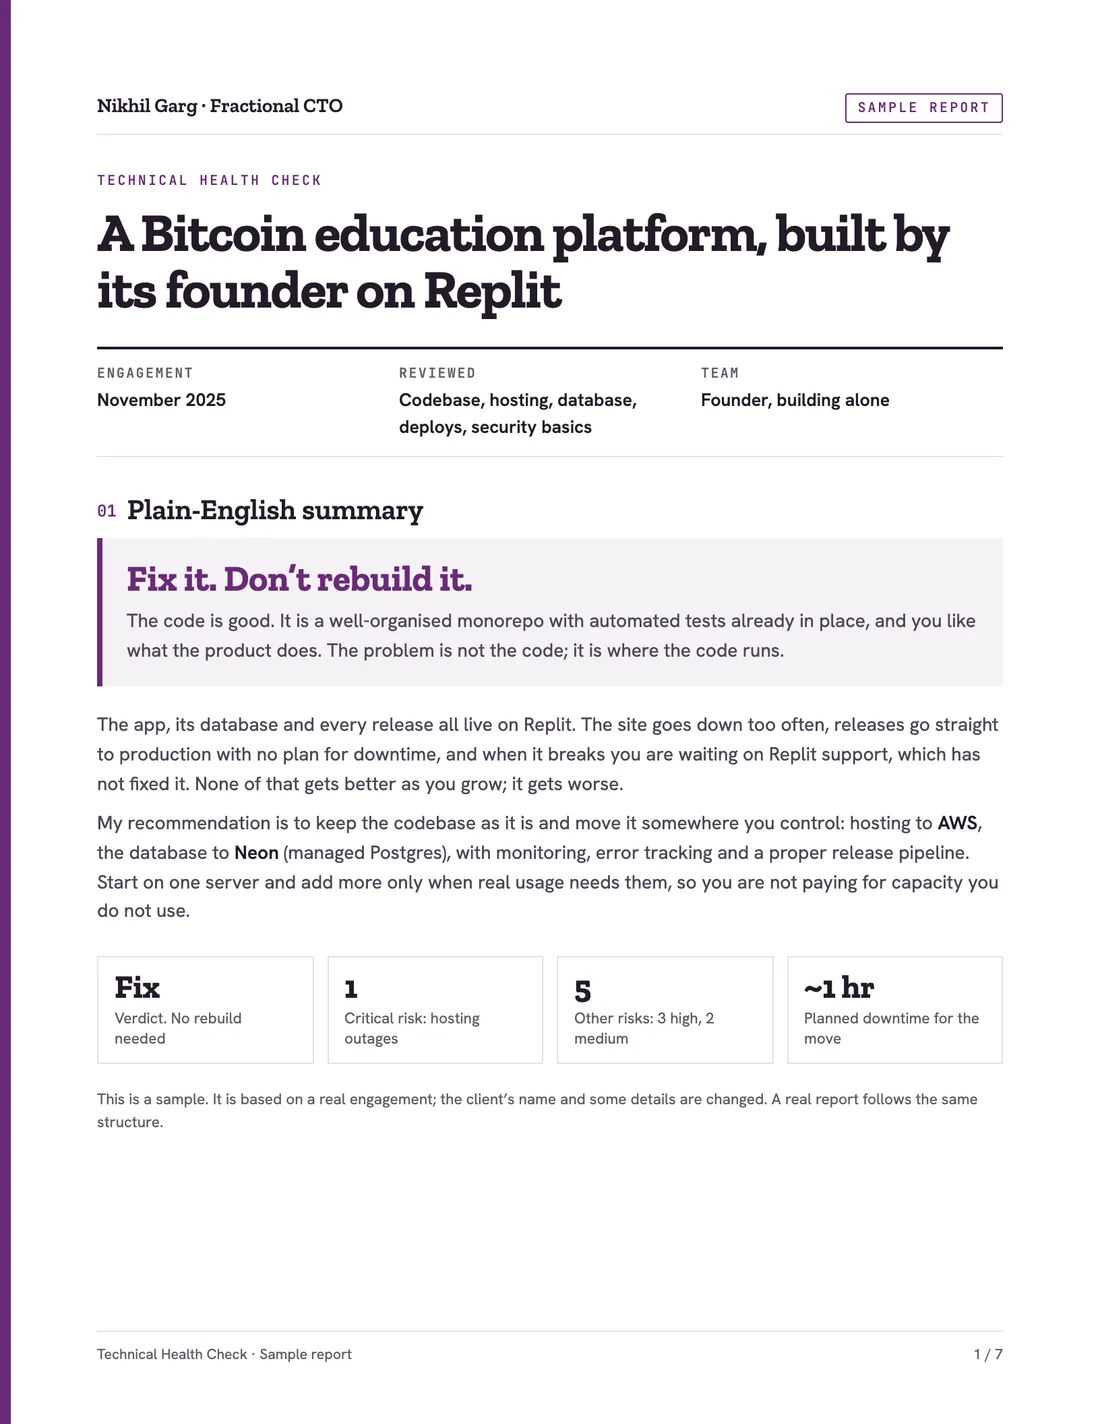
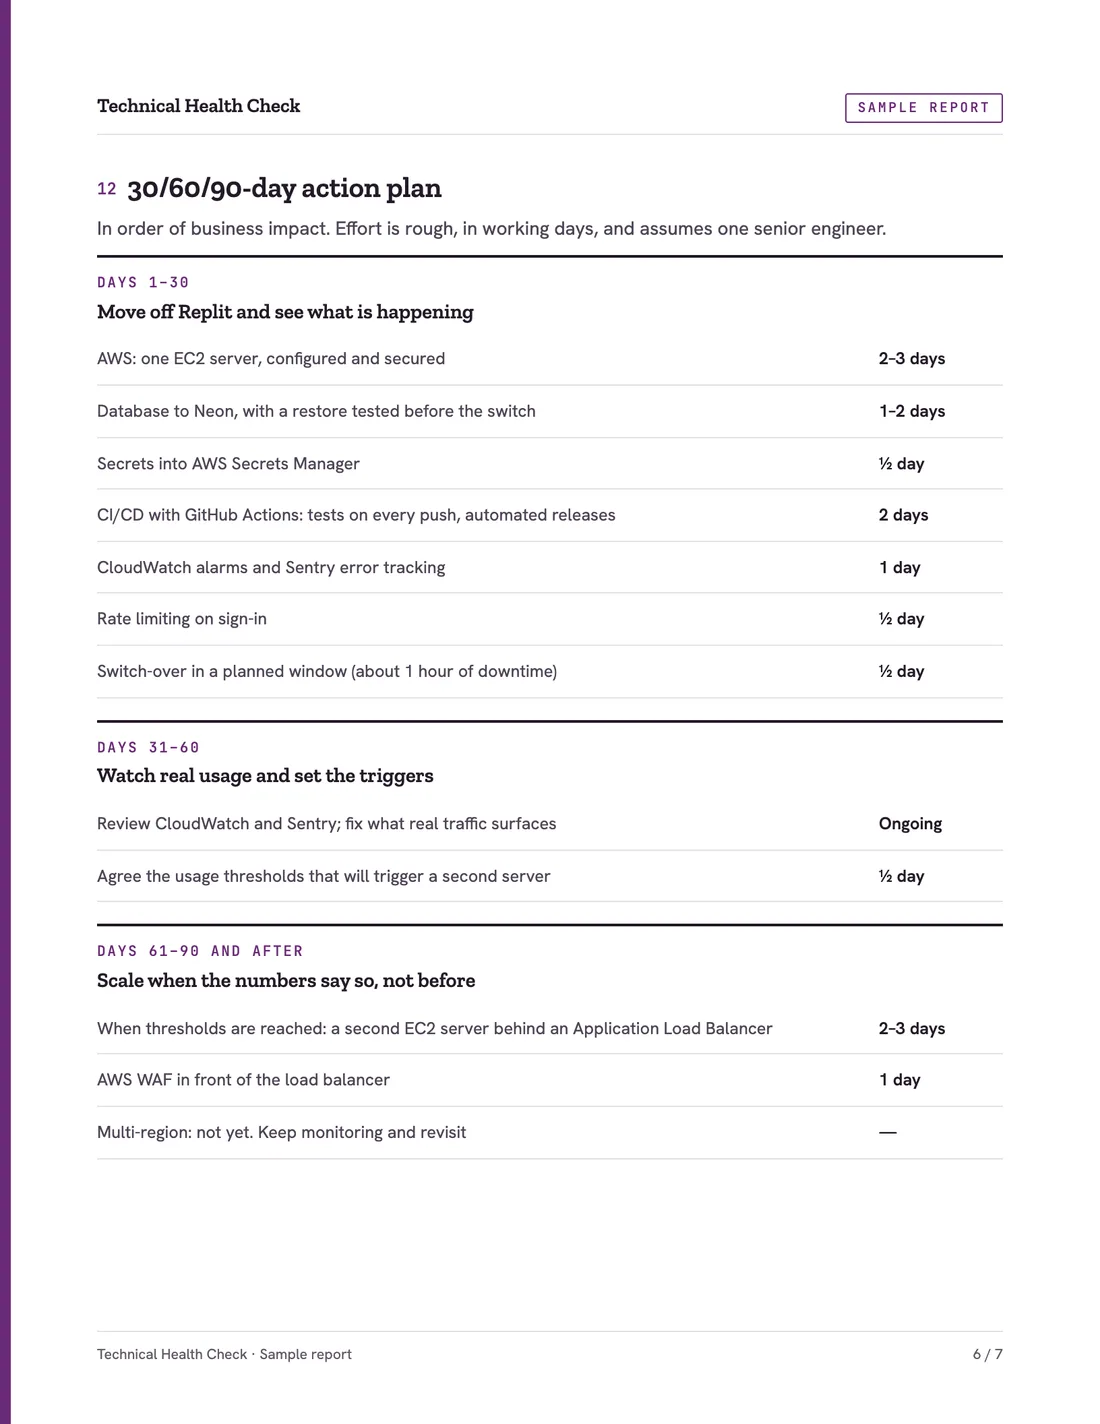
Free. PDF, 7 pages. No email needed.
- Plain-English summary
- What’s solid
- What’s risky, ranked by business impact
- What will break first
- Architecture and data model
- Authentication, access control and multi-tenancy
- Security basics: secrets, permissions, dependencies
- Infrastructure, deployment and scalability limits
- Code quality and test coverage
- Team and vendor delivery
- Recommendation: fix, refactor or rebuild
- 30/60/90-day action plan with rough effort estimates
A sitting CTO who still writes code
The review is done by someone who answers for a production platform today, not by a checklist or a junior reviewer.
CTO at Get Cover
I'm the Chief Technology Officer of Get Cover, a US insurtech whose warranty platform serves 32,000+ clients. The calls I make about your codebase are the same kind I answer for there.
Read the announcementAI prototype to production
I took a vibe-coded Replit app to production-grade AWS, with full CI/CD, load balancing, auto-scaling and security hardening. It now serves 40,000+ users.
Read the case studyThree steps, and nothing is invoiced until fit is confirmed
- Step 1
Tell me about the product
Book a short intro call, or send the intake form below.
- Step 2
I confirm fit and send the invoice
If the Health Check is the right tool for what you need, I confirm it and send the invoice.
- Step 3
Share access, get the report
Once you share read-only access, the written report follows within 5 business days, and we go through it together on a 45-minute call.
$500 fixed. The full fee is credited to your first month of a fractional CTO retainer if you sign within 30 days of receiving the report. See the retainers.
Questions before you book
What is a code audit?
A code audit is a senior review of an existing product at one point in time: how it is built, where it is risky and what will break first. The Technical Health Check is a fixed-fee code audit of the architecture, data model, authentication and access control, security basics, infrastructure, scalability limits, code quality and test coverage, ending in a clear call: fix, refactor or rebuild.
How much does a code audit cost?
It depends on who does it and how deep it goes. The Technical Health Check is a fixed fee, stated at the top of this page, for up to two repositories or one product: a written report within 5 business days, a prioritized 30/60/90-day plan and a 45-minute walkthrough. Nothing is invoiced until I confirm it is the right fit.
Can you audit an app built with Lovable, Bolt, Replit or Cursor?
Yes. A product built in Lovable, Bolt, Replit or Cursor is one of the situations the Health Check is designed for. The review is the same: architecture, data model, authentication, access control, security basics and scalability limits, which is where AI-generated code usually breaks.
What is the difference between a code audit and a code review?
A code review checks a change before it ships. It is part of a team’s routine, and part of my Advisory CTO retainer. A code audit looks at the whole product at one point in time: architecture, security basics, infrastructure, code quality and whether the team or vendor is on track. The Health Check is an audit, written so a non-technical founder can act on it.
What access do you need?
Read-only access is enough, to up to two repositories or one product. I do not need write access or production credentials.
Will you sign an NDA?
Yes. I sign an NDA on request, before you share anything.
How long does it take?
The written report arrives within 5 business days of you sharing access. Then we go through it together on a 45-minute call.
What if everything is fine?
Then the report says so, specifically: what is solid and why, and what to watch as you grow. That is a useful answer to have before you raise, hire or sign the next contract.
What happens after the report?
Nothing, unless you want it to. The action plan is yours to run with your own team or vendor. If you want me to own it, the $500 fee is credited in full to your first month of a fractional CTO retainer if you sign within 30 days of receiving the report.
Is the fee refundable?
No. The fee is not refundable, including if we don’t continue working together after the report.
Is this a technical due diligence review?
It covers the ground a technical due diligence review starts with: architecture, security, code quality, infrastructure and how the work is being delivered. The difference is who it is written for. An investor’s or acquirer’s due diligence is written for them. This report is written for you, so you know what that review would find, and what to fix first, before anyone else looks.
Do you fix things as part of the Health Check?
No. It is a review, not a repair. The report tells you what to fix and in what order, and the 30/60/90-day plan gives rough effort estimates for each item. If you want someone to own the fixes, that is a vibe coding cleanup engagement.
What if my product is bigger than that?
The Health Check covers up to two repositories or one product. If yours is larger, I will tell you on the intro call, before you pay anything.
Know what you have before you spend more on it.
$500 fixed, a written report within 5 business days, and a clear recommendation. The full fee is credited to your first month of a fractional CTO retainer if you sign within 30 days of receiving the report.
A few details are enough to start. I confirm the Health Check is the right fit before anything is invoiced.